Agent registry
See one card per agent product, how many instances connect, and how your policies cover its tools
Questions like "how many people use Claude Code?" or "do our rules cover Codex?" are about an agent product, not one person's client. The registry shows one card per agent product, with how many instances connect and how your policies resolve its tools. In the console, it's the Agent Catalog tab of Inventory › Agents & NHIs.
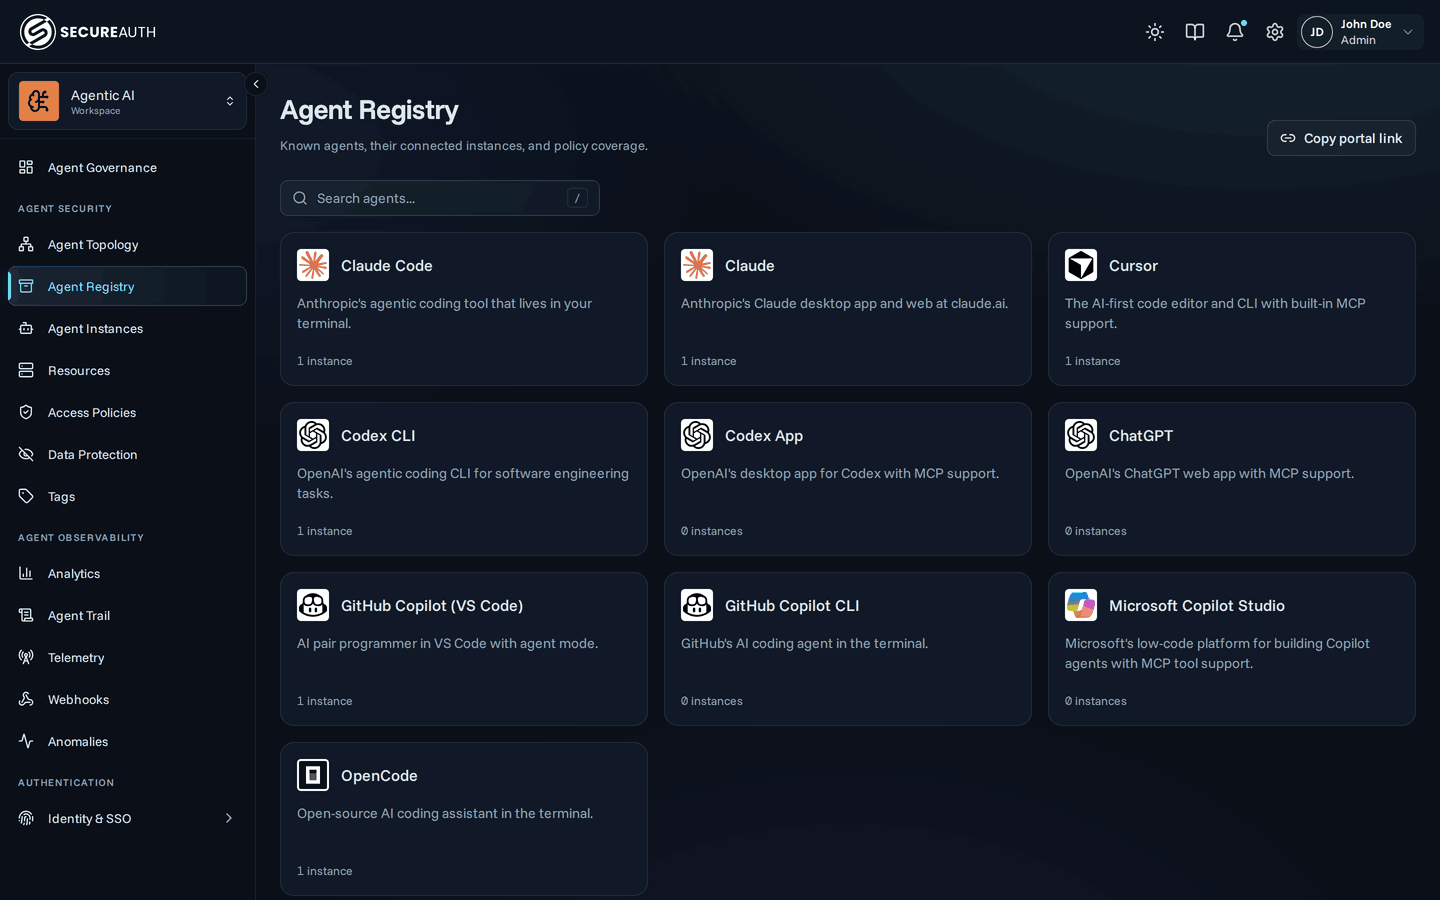
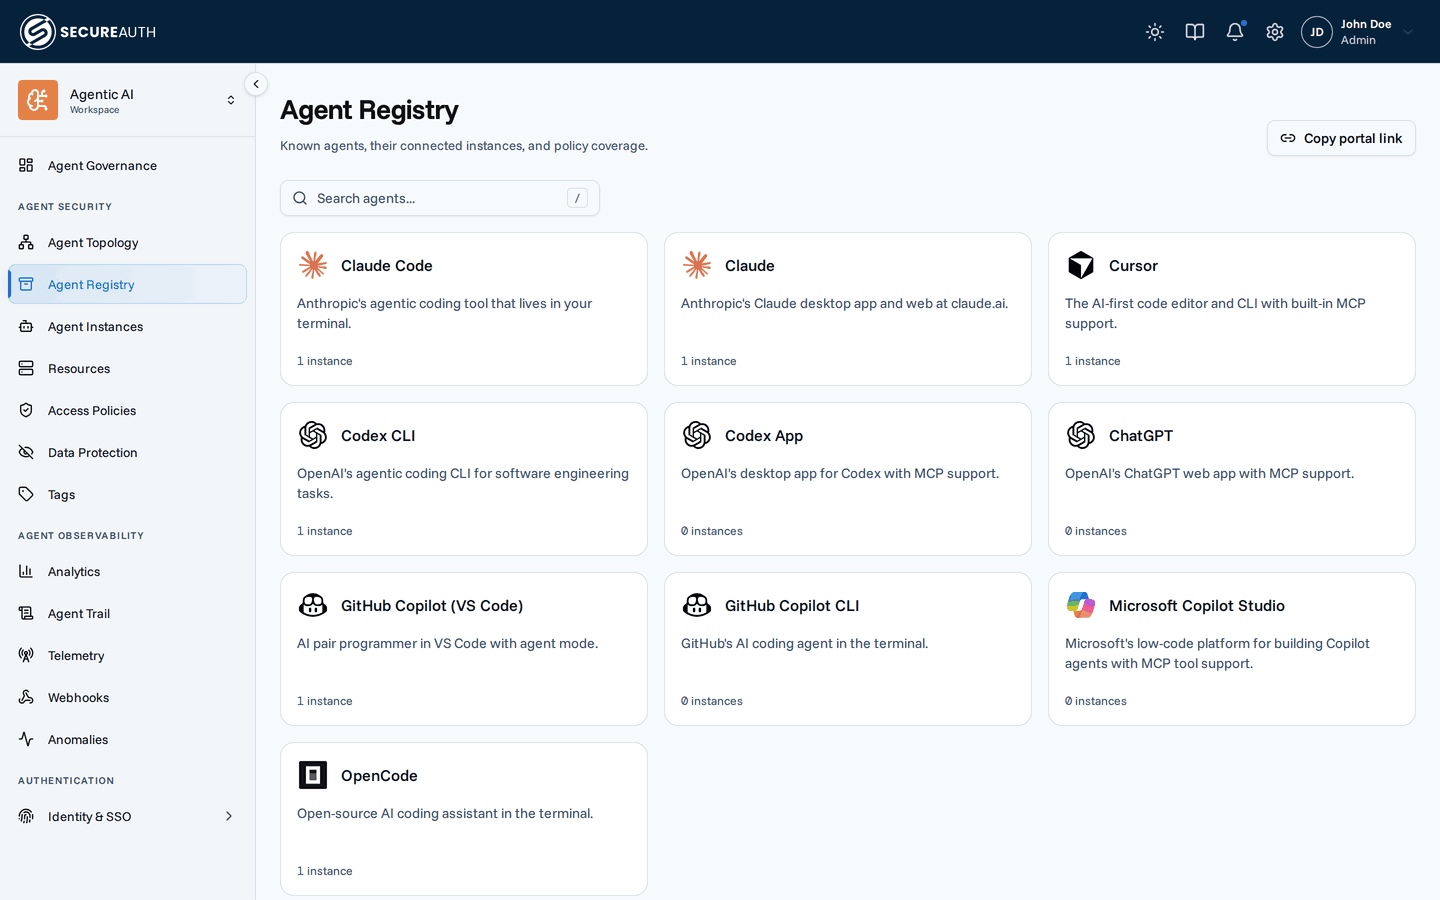
When to use which view
Use the Registry when you want to reason about an agent:
- How many people are using Claude Code in our org?
- Which tools can any Cursor instance call right now?
- Do our policies actually cover Codex, or is it falling through to default-deny?
Use Agents when you want to reason about one person's agent, or a specific connected client of it:
- Why did this one Claude Code session get denied?
- When did this Cursor instance last connect, and from where?
- Disconnect this single instance without affecting other users.
Open an agent
Click a Registry card to open the agent's detail page:
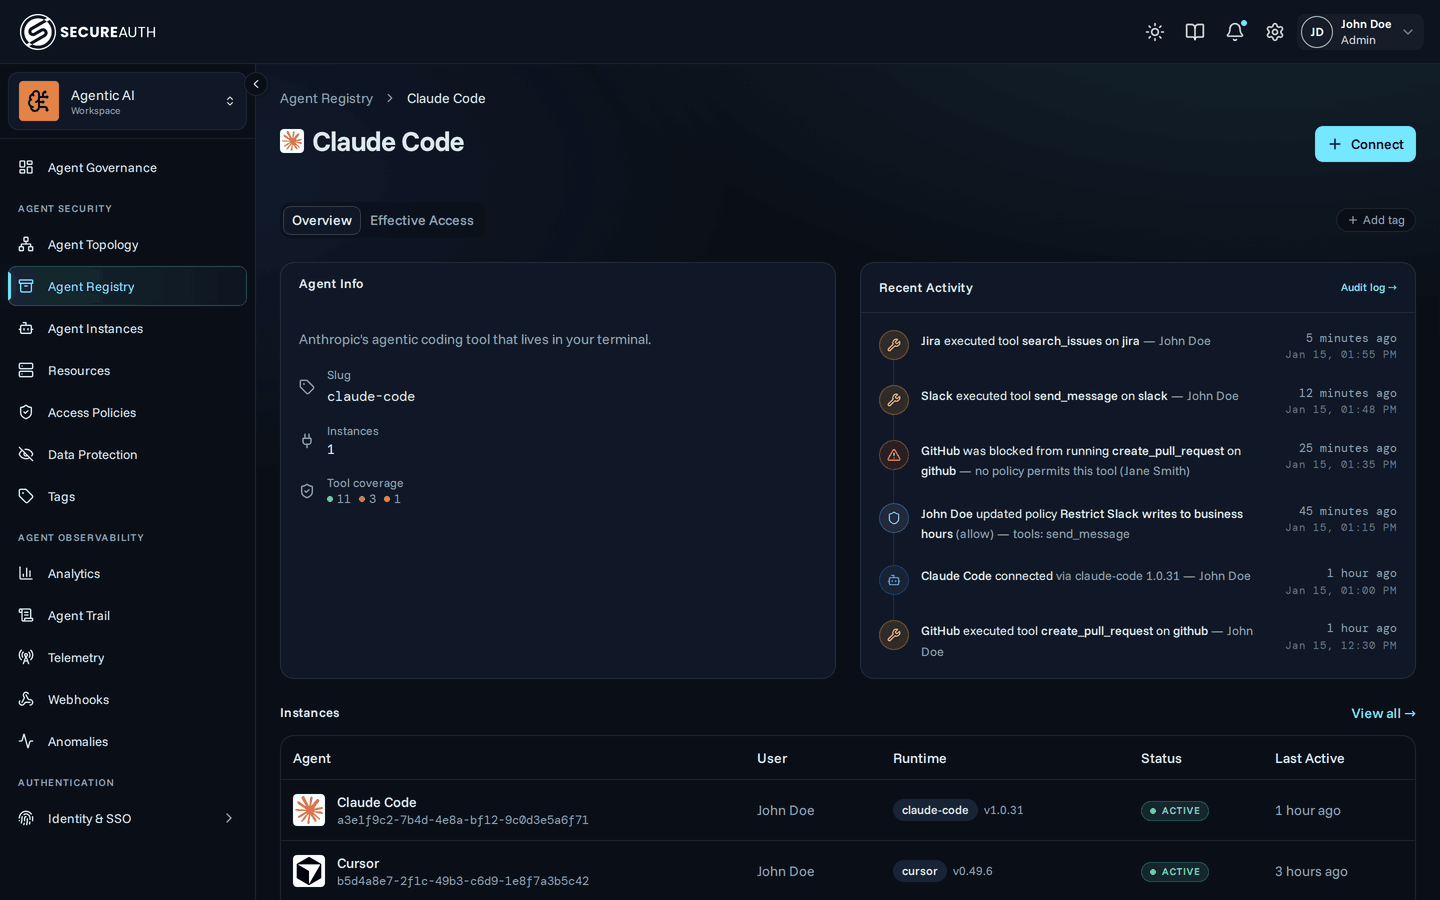
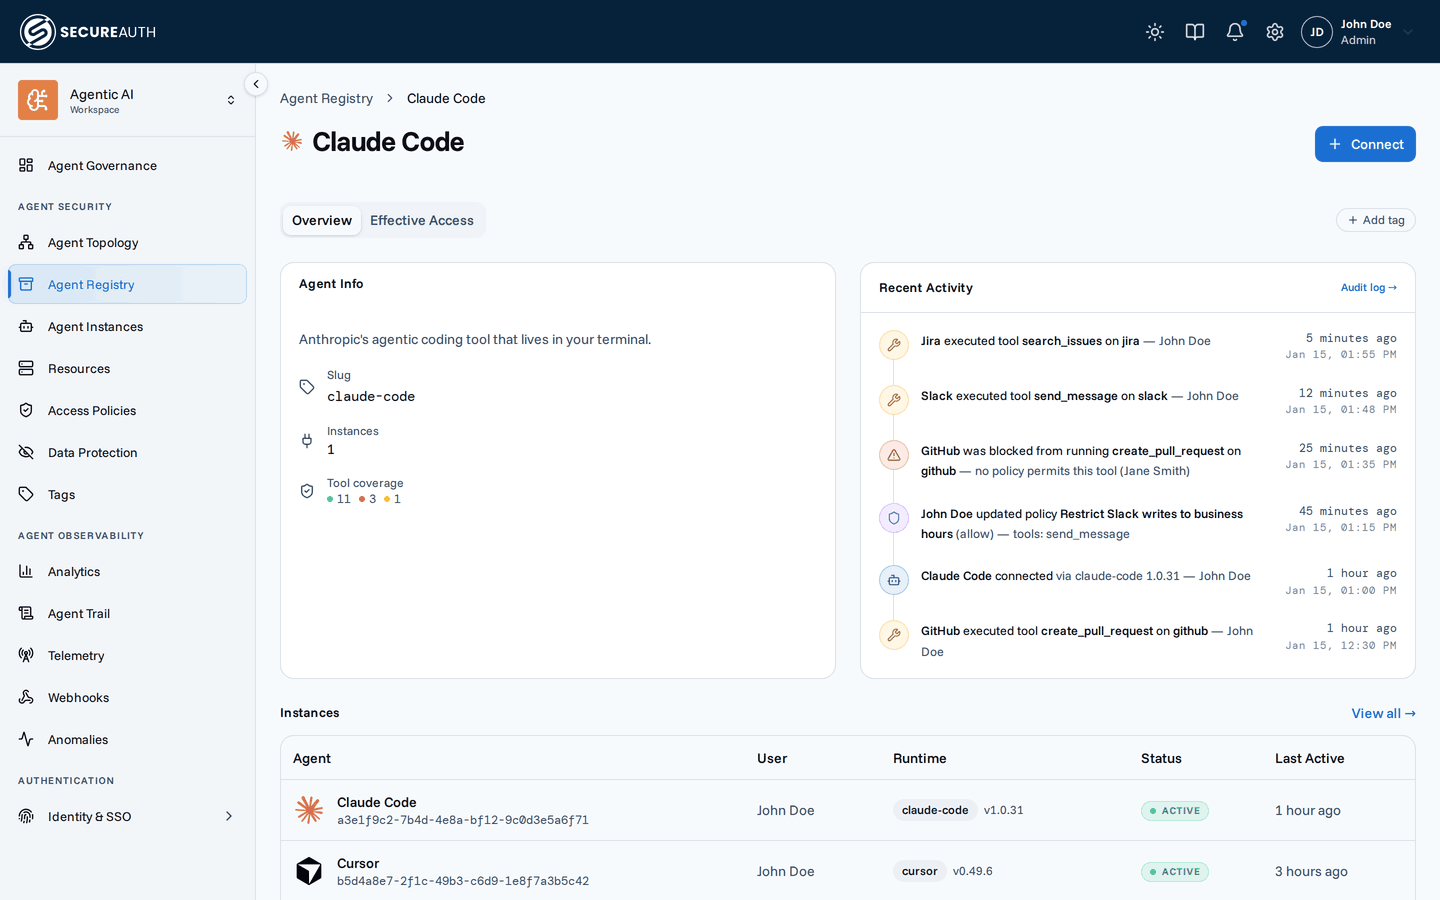
- Overview – agent description, connected-instance count, tool coverage breakdown (allowed / denied / conditional), recent activity, and a table of this agent's ten most recently used instances, with a View all → link to the full list on Agent Instances
- Effective Access – per-MCP, per-tool evaluation for the agent (not a specific instance), useful for previewing what a slug-scoped policy would do without picking one user
The Effective Access tab evaluates policy against the agent's identity alone, not against any specific connected instance. Rules guarded by a CEL condition therefore show as conditional rather than allowed or denied: those conditions need a real instance's request context to evaluate against.
Slug-scoped policies
Both the policy editor and the Registry detail page reference agents by their slug.
A policy scoped to agent.slug == "claude-code" (or via the Agent chip in the rule editor) applies to every Claude Code instance, current and future.
This is the right tool when the rule is about a class of clients rather than a specific user.
Next steps
You can now see how many instances each agent product has and how your rules cover its tools. Next, scope a rule to an agent's slug.
- Policies – write a rule for every instance of an agent
- Connect an agent – how new instances get here in the first place